
Your Copilot Agents Are the New Attack Surface: Live Prompt Injection on Stage
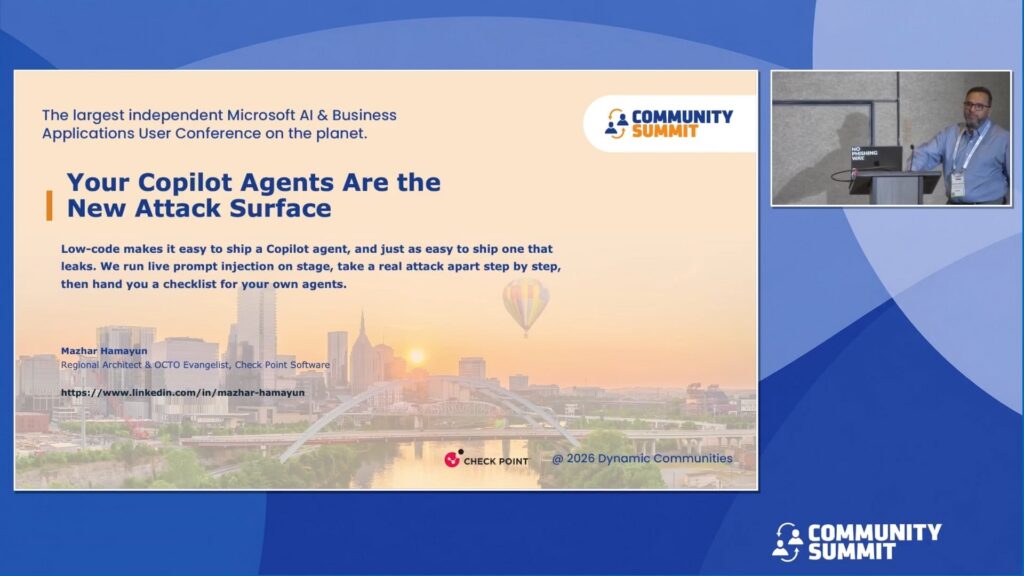
Session Overview: Low-code makes it easy to ship a Copilot agent and just as easy to ship one that leaks data. This hands-on session runs live prompt-injection attacks against a working Copilot Studio agent, shows exactly how data and actions get hijacked, and gives makers a repeatable checklist to red-team and secure their agents before production. Plus a live jailbreak game (Gandalf) attendees can try.
After this session, attendees will be able to:
Recognize the new attack surface an AI agent creates — how the natural-language interface plus connected tools and data turns into prompt injection, data leakage, and hijacked actions, in ways a traditional app doesn’t have.
Explain why a real-world attack (EchoLeak / CVE-2025-32711) slipped past normal app-security controls — and use it to spot the same exposure in an agent they’ve already built.
Run a basic red-team pass on their own Copilot Studio / Power Platform agent using a repeatable checklist — the attacks to try, where injections hide (documents, emails, tool outputs, retrieved content), and what “success” looks like from the attacker’s side.
Apply maker-friendly guardrails before production — least-privilege connectors, input/output screening, human-in-the-loop for high-impact actions, and runtime monitoring
Learning Objectives:
- Recognize the new attack surface an AI agent creates
- Explain why a real-world attack (EchoLeak / CVE-2025-32711) slipped past normal app-security controls
- Run a basic red-team pass on their own Copilot Studio / Power Platform agent using a repeatable checklist
Speakers: Mazhar Hamayun
Recorded at: Community Summit NA 2026
Type: Education Session
Ability Level: 201 – Intermediate
Primary Product: Agents & Copilot
Terms: All rights reserved by the speaker, Community Summit NA, and Dynamic Communities and cannot be reproduced or distributed without express written consent by the speaker and Dynamic Communities.
