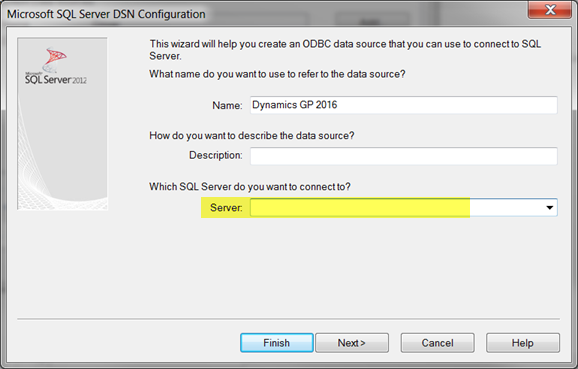
When a new user is setup or an existing user changes their password, GP uses the Server Name in the ODBC connector as a key element of the encrypted password. This is why you have to change everyone’s password when you setup a new server for GP. The actual encryption method is not published by Microsoft but I know this is the variable factor per user.
—————————— Tom Monfre Batteries Plus Bulbs, LLC Hartland WI ————————————————————————-
Rob Klaproth
Member
January 10, 2017 at 12:31 PM
GP encrypts the users password when it is saved to SQL. The user can not use their GP login for any other purposes. If the user tries to login to SQL management studio or other tools they will get an invalid password message as only the GP application can decrypt the password once it is saved.
In addition a salt hash is added to the password with the name of the GP server so when you move to a new server all passwords must be reset.
This encryption insures additional security beyond what SQL does and prevents users from accessing the database outside of the application. This allows you to maintain all security controls inside of GP and not have to deal with anything directly in SQL except when customizations or 3rd party products get installed.
Sent from my iPhone
——Original Message——
Can anyone help me answer a question that my auditors are asking
DO you know how GP handles encryption of passwords
Any help is greatly appreciated
Thanks
Doug
—————————— Douglas Hart Dynamics Administrator Forex Capital Markets New York City NY ——————————
Please note:
This action will also remove this member from your connections and send a report to the site admin.
Please allow a few minutes for this process to complete.

Report
You have already reported this .
Welcome to our new site!
Here you will find a wealth of information created for peopleĀ that are on a mission to redefine business models with cloud techinologies, AI, automation, low code / no code applications, data, security & more to compete in the Acceleration Economy!